Common Cloud Misconfigurations: How to Fix Them and Prove They Stay Fixed
Ten common cloud misconfigurations across AWS, Azure and Google Cloud, read-only commands to find them, and a simple routine for proving each fix stays in place.
In-depth technical analysis from the Pyralink team. Written for UK CISOs, compliance officers, and IT leaders defending against modern cyber threats.
Ten common cloud misconfigurations across AWS, Azure and Google Cloud, read-only commands to find them, and a simple routine for proving each fix stays in place.
Invoice fraud emails now hide instructions for AI email agents. Why filtering won't save you, and the permission and payment controls that will.
What Cyber Essentials v3.3 expects when you run on Google Cloud, the five technical controls mapped to GCP settings, read-only gcloud checks to baseline your projects, and how to keep evidence that fixes stay fixed.
What Microsoft's certificate covers, what you still have to evidence, and a control-by-control checklist of the Azure settings and records an ISO 27001:2022 auditor will sample, with read-only commands to baseline your subscriptions.
What AWS covers, what you still have to prove, and a criterion-by-criterion checklist of the AWS settings and evidence a SOC 2 auditor will ask for, including how to show a fix stayed fixed across a Type 2 period.
Microsoft released an out-of-band .NET update on 25 October 2026 for a Brotli decoder buffer overflow. Most apps are not exposed by default. Here is how to check, patch and keep the evidence.
Copilot does not create new access. It makes existing access searchable. What to check in SharePoint, OneDrive, labels, DLP and logging before you widen a Copilot rollout.
Banning AI does not stop staff using it; it stops you seeing it. A practical method to discover shadow AI, rank the data risk and bring useful tools inside your controls.
ISO/IEC 42001 is the first certifiable standard for AI management systems. What it asks for, how to reuse your ISO 27001 work, and a staged route to audit readiness.
The EU AI Act reaches UK companies that sell AI into the EU or whose AI output is used there. Who is in scope, the revised 2026 timeline, and the steps worth taking now.
ISO 27001 certification is a management system, not a checklist. A practical UK roadmap covering scope, risk assessment, the Statement of Applicability, evidence and the certification audits.
Cyber Essentials is the UK's baseline security certification and a requirement for many public sector contracts. How the process works, what to fix first and how to avoid automatic failures.
Zero trust is a set of design principles, not a product. How UK organisations can apply the NCSC's eight principles across Microsoft 365, Entra ID, Azure and AWS, and where to start.
A penetration test is only as good as its scope. How to define targets, test types and rules of engagement, choose a provider, and get a report your engineers and board can both use.
MDR, managed SOC and managed SIEM are sold with similar language but deliver very different outcomes. What to compare, which log sources matter and the questions to ask before you sign.
Sentinel bills are driven by what you ingest and where you put it. How to use free data sources, table tiers, commitment tiers and pre-SIEM filtering to cut cost without blinding your SOC.
Encryption and tokenisation both protect personal data, but they fail differently. How each works, what UK GDPR says about pseudonymisation, and when to use which, including for AI workflows.
Attackers register domains one character away from yours and impersonate your executives. Why DMARC does not stop it, how to detect lookalikes early, and how to get them taken down.
On-premise, sovereign, air-gapped and data-resident are four different things. What each actually provides, and when a regulator or client will accept it.
Most AI red teaming is jailbreak screenshotting. Here is what a defensible LLM and agent assessment covers, mapped to OWASP, NIST AI RMF and ISO 42001.
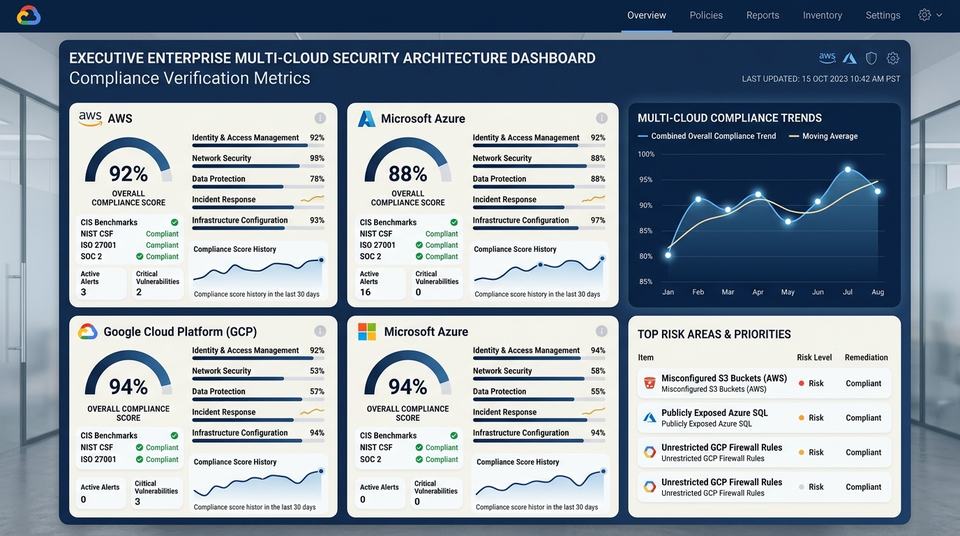
Most cloud compliance work is the same evidence collected five times for five frameworks. Here is why that fails, and what defensible cloud evidence looks like.
Danzell replaced Willow on 27 April 2026. The five controls did not change — the marking did. What auto-fails now, and what evidence assessors expect.
How UK SaaS providers and tech enterprises reduce the manual screenshot scramble by using PyraLink Prove to automate multi-cloud telemetry and prepare evidence for ISO 27001 and SOC 2 audits.
Enterprise procurement teams demand extensive proof before signing major enterprise deals. Here is how PyraLink Prove evidence helps your team answer and defend supplier questionnaires.
Deploying LLMs and autonomous agents exposes enterprises to prompt injection and data exfiltration. Learn how adversarial LLM red teaming and PyraLink Prove infrastructure verification work together.
A large majority of cloud security incidents stem from identity misconfigurations and excessive privileges. Here is how to enforce Zero Trust IAM and use PyraLink Prove for repeatable validation.
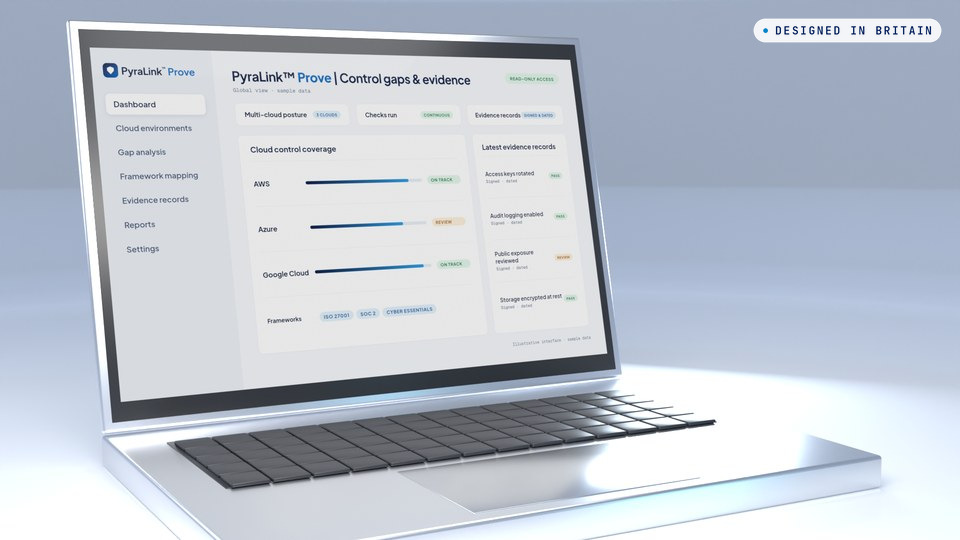
An illustrative workflow showing how PyraLink™ Prove addresses a common audit and supply-chain challenge.

Weekly · Cloud & AI security
Pyralink™ Prove It, by email.
Cloud and AI security notes for UK leaders. Practical and sourced, with no hype.
Request a PyraLink™ Prove demo, or ask about AI Paste Guard and Privacy Harmonize for secure AI adoption.