Four Terms, Four Different Boundaries
Four terms get used interchangeably in AI procurement, and they represent four different technical boundaries. Getting them confused is how organisations end up with a deployment that satisfies a marketing requirement and fails an audit question.
- Data residency means your data is processed and stored within a stated geography. It says nothing about who can technically reach it.
- Sovereign cloud means a hosted service operated within a jurisdiction, often by a locally incorporated entity. It narrows legal exposure. The operator is still a third party with technical access paths.
- On-premise means the software runs on infrastructure you control. Many on-premise AI products still require outbound connectivity — for model serving, licence validation, or telemetry.
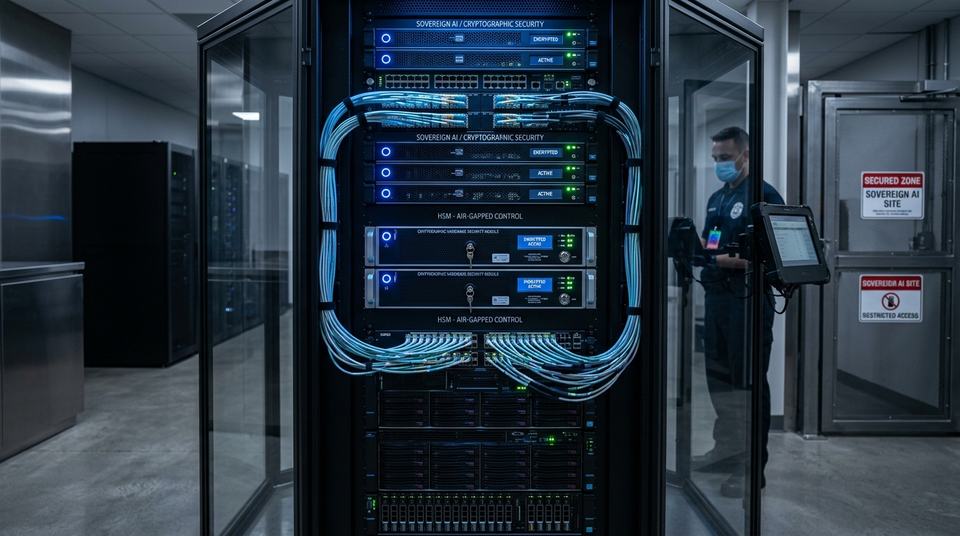
- Air-gapped means there is no path out. After installation, the system makes no external calls: no model vendor API, no licence callback, no telemetry. Model weights, inference, retrieval indexes and orchestration all sit inside your boundary.
The axis that separates these is not where the data sits. It is who can technically reach the model and the data — as distinct from who has contractually promised not to. That is a control question, and control questions are the ones that survive an audit.
Who Actually Needs the Strict Version
Air-gapped deployment is expensive relative to an API call. It is justified in a narrow but growing set of circumstances, and it is worth being honest about which you are in.
- Contractual prohibition: Your client's contract, or your own data processing agreement, forbids transfer of certain categories of data to third-party processors. This is a common driver, and it is often discovered mid-deal rather than at design time.
- Regulated categories: Health records, legal privilege, criminal justice data, classified material, safety-critical operational data. Here the constraint tends to be absolute rather than risk-weighted, and no amount of encryption-in-transit argument moves it.
- Confidentiality of the input itself: Source code, unfiled patents, deal documents, trading positions, defence-adjacent engineering data. The sensitivity is not in a personal data category — it is that the content has commercial value to whoever sees it.
- Determinism and continuity requirements: Systems that must behave identically over long periods, or must keep functioning without external dependencies. If a vendor deprecates a model version, cloud-dependent behaviour changes underneath you. Local weights do not.
If none of those apply, a well-governed cloud deployment with proper contractual and technical controls is usually the correct answer. Sovereignty theatre — an isolated deployment procured to satisfy a stakeholder's instinct rather than a requirement — is real cost for no control benefit.
What You Give Up, Stated Honestly
Vendors selling private AI tend to skip this section. It is the section that determines whether the project succeeds.
- Capability gap: Open-weight models have narrowed the distance to frontier systems considerably, but the distance is not zero, and it moves. For summarisation, extraction, classification, retrieval-grounded question answering and structured drafting — which is the great majority of enterprise workload — the gap is rarely the binding constraint. For frontier reasoning tasks, it can be.
- You now operate infrastructure: GPU capacity, model lifecycle, index maintenance, monitoring, patching, capacity planning. This is a running operational commitment, not a deployment. Organisations that treat it as a project and disband the team afterwards end up with an unpatched inference stack holding their most sensitive data — a worse position than where they started.
- Updates require a process: In a true air gap, every model update, dependency upgrade and security patch arrives through a controlled transfer process you have to design, document and staff. That process is itself an attack surface and an audit subject.
- The security boundary is not automatic: Air-gapping removes external network exfiltration paths. It does not remove privilege escalation, over-permissioned retrieval, prompt injection through ingested documents, or an agent with more tool access than its task requires. An isolated agent that can read every document in the estate and is manipulable through the documents it reads is still a serious problem — it is just an internal one. The same adversarial testing discipline applies.
The Architecture, in Control Terms
Described as controls rather than components, an air-gapped deployment needs:
- Local inference: Open-weight models served on your hardware, inside your boundary, with no external call path at runtime.
- Local retrieval: Documents embedded and indexed on your infrastructure, enforcing the source system's least-privilege permissions.
- Scoped tool access: Any action-taking capability constrained to least privilege, with identity tied to the requesting user rather than a shared service account.
- Full audit trail: Prompts, retrievals, tool calls, and outputs logged and retained inside the boundary.
- A controlled update path: Documented, authorised, verified, and logged.
Where the Regulatory Picture Is Heading
The EU AI Act's transparency obligations under Article 50 became applicable on 2 August 2026, with the marking and detection requirement reaching systems already on the market from 2 December 2026. High-risk obligations were deferred by Regulation (EU) 2026/1744 — published in the Official Journal on 24 July 2026 — to 2 December 2027 for standalone Annex III systems and 2 August 2028 for AI embedded in Annex I regulated products. The deferral buys documentation time; it does not remove the documentation.
In the UK, the Cyber Security and Resilience Bill, introduced in November 2025, cleared the Commons and entered the Lords in June 2026. It puts managed service providers and designated critical suppliers into a statutory regime with expanded incident reporting duties, and it places the NCSC's Cyber Assessment Framework on a firmer footing.
For AI deployment decisions, the practical read is this: the questions your clients will ask about your AI systems are converging on the questions regulators ask about your other systems. Where does the data go, who can reach it, what did the system do, and can you prove it. An isolated deployment answers the first two structurally. The last two you still have to build.
Further reading: Tokenisation vs Encryption Under UK GDPR: Which Protects Personal Data Better, and When? and ISO/IEC 42001 Readiness: A Practical Guide for UK Organisations Building an AI Management System.
Where the Pyralink Products Fit
Pyralink builds products for secure AI adoption. AI Paste Guard checks text pasted into AI chat tools locally in the browser.
Request a Demo ↗Sources: Regulation (EU) 2024/1689 (EU AI Act) and Regulation (EU) 2026/1744 (Digital Omnibus on AI, in force 27 July 2026); Cyber Security and Resilience (Network and Information Systems) Bill, UK Parliament; OWASP GenAI Security Project agentic risk taxonomy.