The Cloud Evidence Problem
Most organisations do not have a cloud security problem. They have a cloud evidence problem.
The controls are usually there. Encryption is on. Logging is enabled. Access is roughly least-privilege. What is missing is the ability to demonstrate any of it to a third party — an auditor, an enterprise procurement team, an insurer — within the window they have given you, in a form they will accept.
That gap is expensive in a specific and measurable way: it delays revenue. A supplier security questionnaire arriving mid-deal with a seven-day turnaround is not a compliance task. It is a commercial deadline with a compliance cost attached.
The Duplication Problem Nobody Budgets For
Consider what a mid-sized UK organisation running AWS and Microsoft 365 is typically asked to evidence in a given year:
- ISO 27001 surveillance audit
- Cyber Essentials or Cyber Essentials Plus renewal
- SOC 2 readiness for a US customer
- A UK GDPR record of processing activities and technical measures
- Two or three enterprise supplier questionnaires
- A cyber insurance renewal questionnaire
Six or seven exercises. Each asks for a different framework's vocabulary. And underneath, they are asking about the same forty or fifty technical facts: who has privileged access, what is exposed to the internet, how quickly patches land, whether MFA is universal, whether logs are retained and where. Yet almost every organisation re-collects the facts each time, from scratch, by hand.
Why Provider-Native Tooling Does Not Close the Gap
- They are single-cloud by design: A finding in one provider's console does not reconcile with another. Reconciling them is manual work, where errors enter evidence.
- They speak benchmark, not framework: Provider-native tools map to CIS. Auditors ask about ISO 27001 Annex A controls, ISO 27017, or SOC 2 trust services criteria.
- They produce findings, not decisions: A list of 400 misconfigurations sorted by severity is a work queue, not evidence. An audit committee needs a defensible statement of control effectiveness.
What Defensible Cloud Evidence Actually Looks Like
- Derived from live environment via read-only APIs: An observation from a live cloud API can be digitally signed and dated, which a screenshot cannot be.
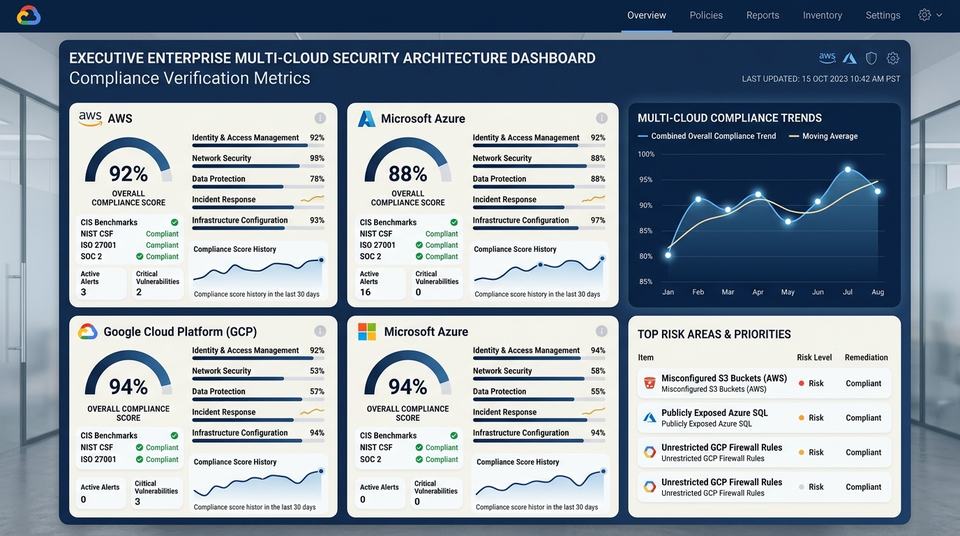
- Mapped once and reused many times: Harvest configuration state once, then map it simultaneously across ISO 27001, SOC 2, Cyber Essentials, NIS2 and DORA in PyraLink™ Prove.
- Repeatable: Repeated scans turn point-in-time assertions into a dated history that surveillance auditors can review.
- Portable and attributable: Digitally signed, dated evidence records that third parties can verify independently, without needing access to your production accounts.
Comparing tools? See how PyraLink Prove compares with Vanta, Drata and Wiz, with every competitor fact linked to its source.
Preparing a SOC 2 report on AWS? Our SOC 2 on AWS controls and evidence checklist maps each criterion to the AWS settings and evidence auditors ask for.
The Commercial Business Case
Deal Velocity: Move through enterprise procurement security reviews without stalling.
Audit Cost: Reduce external auditor time spent chasing missing evidence.
Board Defensibility: Directors sign compliance declarations backed by verifiable monthly evidence records.
Further reading: ISO 27001 Certification in the UK: A Practical Readiness Roadmap from Gap Analysis to Stage 2 and Zero Trust Architecture in Practice: Applying the NCSC's Eight Principles to Microsoft 365, Azure and AWS.
Fixing findings is only half the job. Our guide to common cloud misconfigurations and how to prove they stay fixed covers ten settings to check across AWS, Azure and Google Cloud.
Need Article 21 evidence from AWS, Azure and Google Cloud? Our NIS2 cloud compliance checklist maps each measure (a–j) to the artefacts auditors ask for.
Automate Multi-Cloud Compliance with PyraLink Prove
PyraLink Prove performs multi-cloud security auditing across AWS, Azure, and Google Cloud using temporary, read-only access.
Request a PyraLink Prove Demonstration ↗Pyralink Innovation Ltd is registered in England & Wales (14512137), ICO registered, and carries professional indemnity cover. PyraLink™ Prove access is read-only; see our Trust Centre for details.