The Screenshot Scramble: Why Manual Cloud Auditing Fails
Every fast-growing UK business and technology enterprise faces the same recurring audit headache: an upcoming ISO/IEC 27001:2022 surveillance audit, an annual SOC 2 Type II assessment, or a critical Cyber Essentials Plus certification. Traditionally, this triggers a painful, weeks-long scramble where senior DevOps, cloud architects, and engineering leaders are pulled away from product delivery to manually take screenshots of AWS IAM policies, Azure Network Security Groups, and GCP storage buckets.
Manual compliance gathering introduces three critical business liabilities:
- Stale Point-in-Time Evidence: A screenshot captured today is obsolete the moment a developer merges an infrastructure-as-code change tomorrow.
- High Opportunity Cost: Senior engineering time goes on gathering screenshots by hand instead of building the product.
- Unseen Configuration Drift: Manual sampling inevitably misses subtle misconfigurations, such as unlogged S3 buckets, excessive IAM trust relationships, or unencrypted storage volumes.
Enter PyraLink™ Prove: Automated Multi-Cloud Telemetry
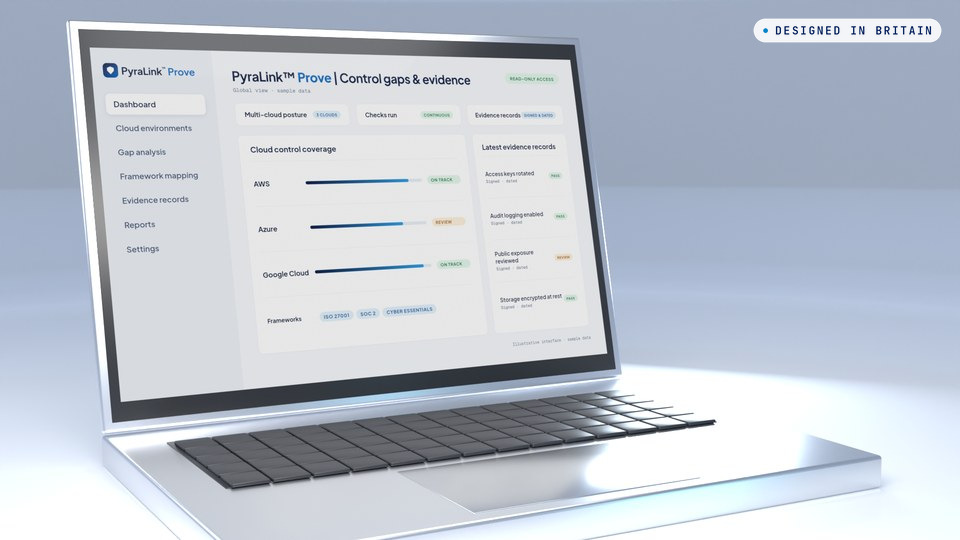
To eliminate this friction, Pyralink engineered PyraLink™ Prove—our flagship compliance automation platform designed by a team holding CISM, CISA and CEH certifications. PyraLink Prove connects directly to your cloud environments using strictly scoped, read-only IAM connectors (requiring zero agent installation on endpoints or servers) to collect and analyse cloud configuration evidence on every scan.
PyraLink Prove evaluates cloud security controls across AWS, Microsoft Azure, and Google Cloud, mapping every configuration directly into formal audit artifacts aligned with ISO 27001, SOC 2 and Cyber Essentials.
Comparing tools? See how PyraLink Prove compares with Vanta, Drata and Wiz, with every competitor fact linked to its source.
Preparing a SOC 2 report on AWS? Our SOC 2 on AWS controls and evidence checklist maps each criterion to the AWS settings and evidence auditors ask for.
How PyraLink Prove Transforms Your Audit Workflow
- Zero-Agent Read-Only Ingestion: Connect AWS, Azure, or GCP using temporary, read-only IAM roles with zero disruption to live production workloads.
- Control Cross-Mapping: Single telemetry points (such as MFA enforcement or database encryption) are automatically mapped across multiple compliance frameworks simultaneously.
- Digitally Signed Evidence Reports: Generate digitally signed, dated evidence records that you can verify independently, structured for review by external certification bodies and enterprise buyers.
Pairing PyraLink Prove with Your Audit Programme
PyraLink Prove supports audit readiness by automating internal audit evidence preparation, so your team and your auditor work from the same record.
Related Pyralink Products & Guides
PyraLink Prove sits alongside the other Pyralink products. Explore how signed audit evidence connects to them:
- Discover how PyraLink Prove evidence helps Defend Customer InfoSec Questionnaires with Evidence.
- Read our guide to Zero Trust Cloud IAM on AWS and Azure.
Further reading: ISO 27001 Certification in the UK: A Practical Readiness Roadmap from Gap Analysis to Stage 2 and How to Get Cyber Essentials Certified: A Step-by-Step Guide for North East Organisations.
Ready to Automate Your Next Cloud Audit?
Request a technical demonstration of PyraLink Prove to see how quickly your AWS and Azure environments can produce audit-ready evidence.
Request a PyraLink Prove Demo ↗